Listen to this article
Take the story with you. Choose a voice and a pace that suits you.
Or listen in another language / choose a voice
Getting your device voices ready…
The voice follows the displayed language and your browser’s regional preference when available. You can choose another narration voice.
The EU AI regulatory sandbox rules are now fixed. The European Commission adopted Implementing Regulation (EU) 2026/2487 on 10 November 2026, published it in the Official Journal on 11 November, and it enters into force on 1 December 2026 (EUR-Lex). Every member state must have at least one national sandbox operating by 2 August 2027, and they will all admit, charge and sign off firms under the same rulebook.
Information verified through 18 November 2026.
A sandbox, in the AI Act’s design, is a controlled framework run by a national authority. Inside it, a provider can develop, train, validate and test a system — including in real-world conditions — under regulatory supervision for a limited time before the system reaches the market (Cloud Security Alliance). The point is legal certainty, not a shortcut. The regulation’s recitals say sandboxes should help innovators comply with the AI Act and, where relevant, other law such as the GDPR (EUR-Lex).
An AI Act sandbox free for SMEs, priced for everyone else
The pricing is the headline for small companies. The AI Act sandbox free for SMEs commitment is written into the regulation: small and medium-sized firms, start-ups included, get priority access and free regulatory guidance, advice and supervision, including supervision of testing in real-world conditions. Authorities may recover only exceptional costs, and then only with advance notice and a detailed invoice (EUR-Lex). The same pricing applies to public authorities and bodies.
Larger firms can be charged up to the full cost of the services, with fees published when applications open. Providers with no registered office or branch in the EU must pay a participation fee and appoint an authorised representative in the Union under a written mandate (AISecPlat).
Eligibility is broad. A provider or prospective provider may apply for a system not yet on the market, a system already on the market that will be substantially modified, or a system that becomes high-risk because its use changes. Applicants are not limited to their own member state (AISecPlat). Authorities must decide within three months of a complete application, weighing five criteria: the regulatory challenge, the potential for regulatory learning, the public interest, the maturity of the proposal and how innovative the system is (Cloud Security Alliance).
Each project then runs on an agreed sandbox plan covering objectives, responsibilities, the legal requirements being tested, risk safeguards, serious-incident procedures and any real-world testing. Authorities may suspend a project if the plan is breached or if risks to health, safety or fundamental rights cannot be mitigated (AISecPlat).
The Implementing Regulation 2026/2487 exit report — useful, and limited
What a firm leaves with is two documents. The written proof lists what was done and which requirements were assessed. The exit report, due within 45 working days of the end of participation, describes the regulatory questions examined, how they were resolved, serious incidents and lessons that can be reused (AISecPlat).
Those documents travel. Market surveillance authorities and notified bodies across the EU must recognise them and take them positively into account in conformity assessment (Cloud Security Alliance). That is a real benefit. It is not approval.
AI regulatory sandbox no conformity status, and no liability shield
Here is the part applicants should read twice: AI regulatory sandbox no conformity status attaches to either document. Neither the written proof nor the exit report has the legal effect of an EU declaration of conformity, and completing a sandbox does not mean a system is cleared for sale (AISecPlat).
Liability stays put, too. Participants remain liable under EU and national law for damage to third parties during testing. Protection is limited to administrative fines, and only where the participant observed the sandbox plan and followed the authority’s guidance in good faith (Cloud Security Alliance). The CSA analysis also notes that the regulation prescribes no fixed catalogue of security tests — the sandbox plan, negotiated project by project, defines what testing happens.
Timing is tight in a way the December start date hides. National sandboxes are not due until 2 August 2027, yet high-risk obligations for stand-alone systems apply from 2 December 2027, and for AI embedded in regulated products from 2 August 2028 (AISecPlat). The CSA notes that, as of May 2026, only one of the 27 member states — Spain — had an operational sandbox (Cloud Security Alliance). If most sandboxes open close to the deadline, firms wanting an exit report to inform conformity work may have only months in hand.
Analysis: The design is deliberately modest. Brussels has standardised the doorway — one set of entry rules, a three-month decision, a recognisable exit document — without lowering the bar behind it. For a small firm building a hiring, credit or health system, free supervised testing is still the cheapest regulatory advice it will ever get. The risk is capacity, not intent: twenty-seven national programmes, most starting from near zero, against a December 2027 clock.
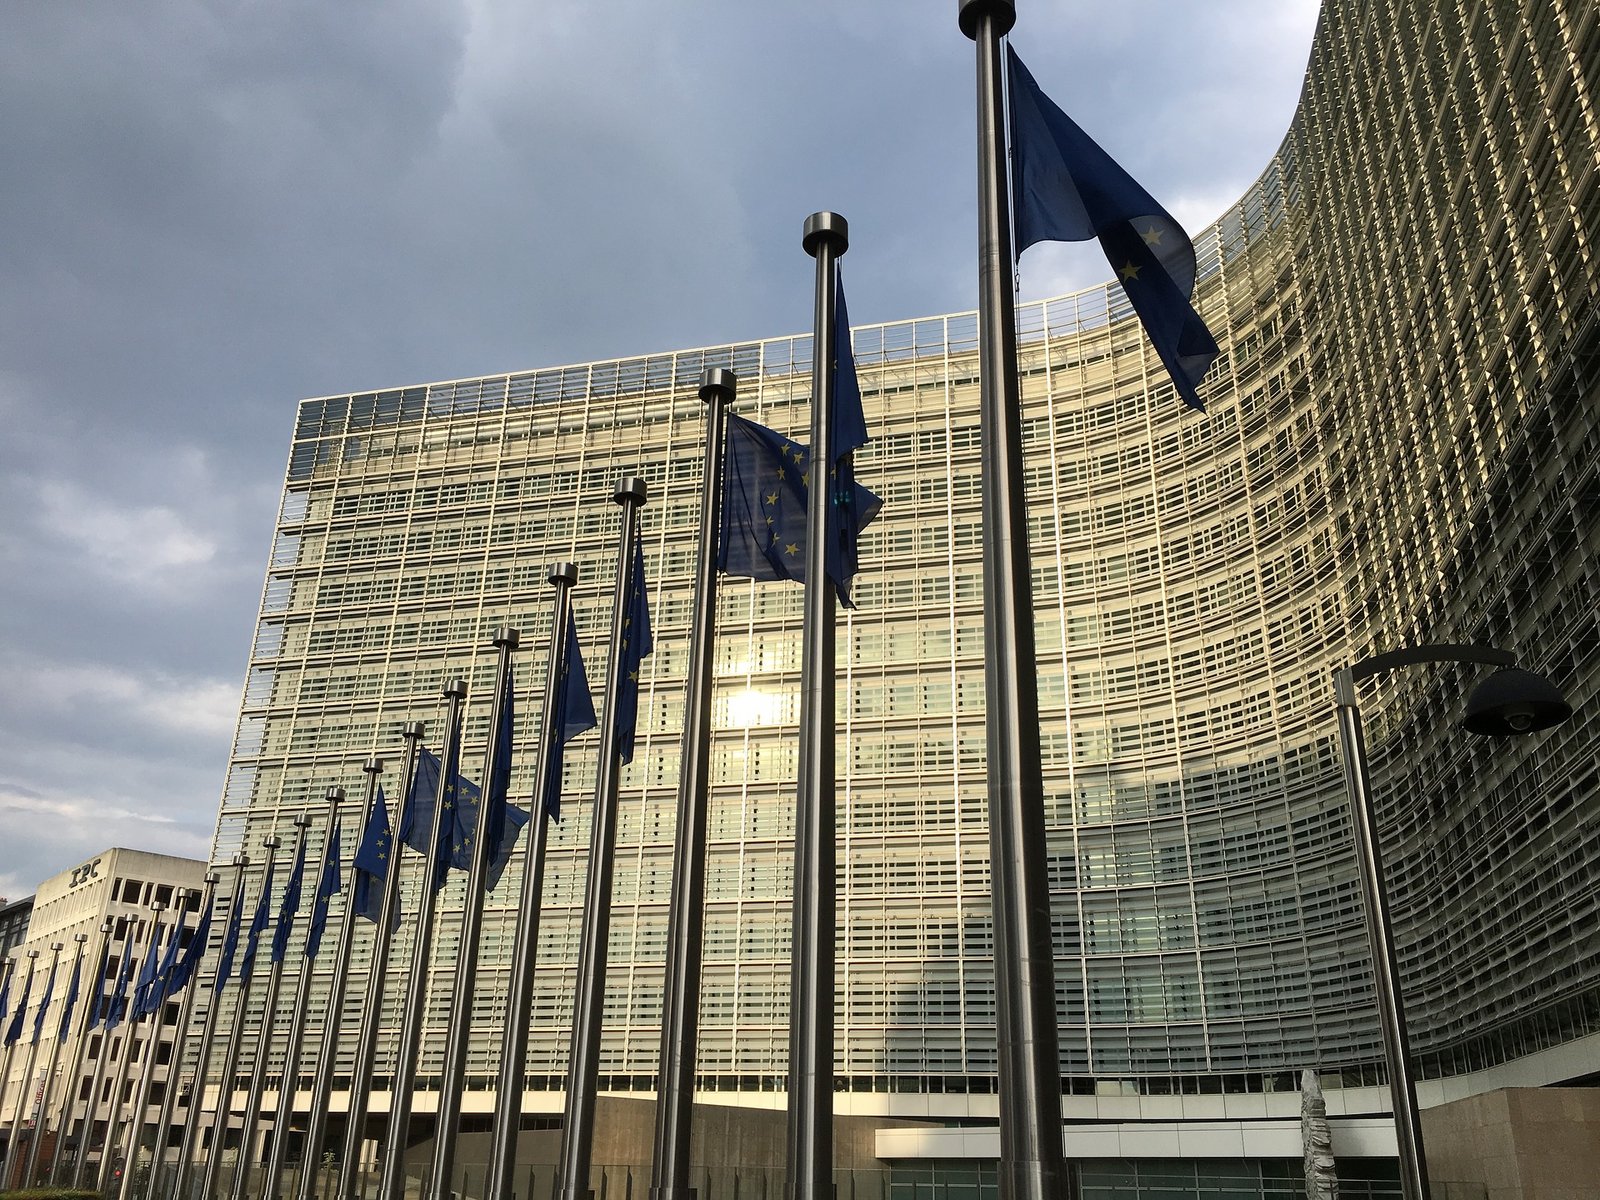
Photo: The Berlaymont building, headquarters of the European Commission in Brussels, via Wikimedia Commons (CC0)
Sources
- EUR-Lex — Commission Implementing Regulation (EU) 2026/2487 — https://eur-lex.europa.eu/eli/reg_impl/2026/2487/oj/eng
- Cloud Security Alliance — Sandboxes Without Safe Harbor: EU AI Sandbox Rules and Security Testing — https://labs.cloudsecurityalliance.org/research/csa-research-note-eu-ai-regulatory-sandbox-rules-20261112-cs/
- AISecPlat — EU Sets AI Act Sandbox Rules: Free Entry for SMEs, 3-Month Decisions, EU-Wide Exit Reports — https://www.aisecplat.com/blog/eu-ai-act-regulatory-sandbox-rules-2026-2487-explained
Leave a comment
Comment as a guest and verify your email, or sign in or create a reader account. Guest comments reach our review queue after email verification; account holders can submit directly for review.